
The Server That Was Out of Scope Until Patch Tuesday
A scope label held for eleven months. Then one maintenance window exposed the administrative path everybody had stopped seeing.
Open the case fileA practitioner’s field guide to PCI DSS complexity
The Cluster of Wack is where undocumented dependencies, inherited exceptions, vague ownership, and unsupported scope assumptions all meet. We give the chaos a name—and a way out.
No generic compliance advice. Just practitioner-grade clarity.
Does this sound familiar?
Centerpiece model / formation integrity
Scope, applicability, implementation and responsibility, and evidence cannot tell four different stories about the same environment. The Diamond Fulcrum shows what moves when one fact changes.
Enter the Diamond FulcrumVisual field model / TPSP reliance
A provider can perform the activity. You still need an exact service, a responsibility seam, current evidence, customer controls, and a fact-specific map of the infrastructure that remains.
Explore the deferral boundary01 / The vocabulary
If practitioners can name the pattern, they can stop treating every symptom as an isolated surprise. Start with the current canonical terms.
Accumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open field guide →The extra operational and assessment effort created by unnecessary complexity.
Open field guide →The tendency of one workaround to attract more systems, processes, and dependencies.
Open field guide →How far one questionable component or dependency expands PCI DSS scope.
Open field guide →The concentration of assumptions, exceptions, and unclear dependencies around a component.
Open field guide →When a temporary exception becomes a template and eventually becomes standard architecture.
Open field guide →A configuration nobody currently owns and everyone is afraid to change.
Open field guide →When “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open field guide →A system considered both in and out of scope depending on which evidence request is being answered.
Open field guide →The belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open field guide →The growing distance between the environment that exists and the diagrams used to explain it.
Open field guide →Reconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open field guide →The quiet expansion of an exception beyond its original time, systems, owners, or approved conditions.
Open field guide →Treating a scope label in a worksheet as the reasoning that makes the label true.
Open field guide →A responsibility model with many participants but no person accountable for the current decision or result.
Open field guide →Two control activities treated as interchangeable because their labels look alike while their coverage does not.
Open field guide →A convincing sample drawn from a population whose completeness and variants were never established.
Open field guide →Presenting adjacent safeguards as a compensating control without demonstrating the required constraint, rigor, and equivalence.
Open field guide →The same underlying artifact repeated across control claims until repetition is mistaken for corroboration.
Open field guide →Attempting to transform an unresolved applicability question into an exclusion by changing its spreadsheet status to N/A.
Open field guide →Wack law / 00
“Wack cannot be eliminated merely by changing its status to N/A in a spreadsheet.”
The Wack Conservation Principle
02 / The method
The joke earns attention. The method earns trust. Move from “it’s complicated” to a defensible story that architecture, responsibility, and evidence all agree on.
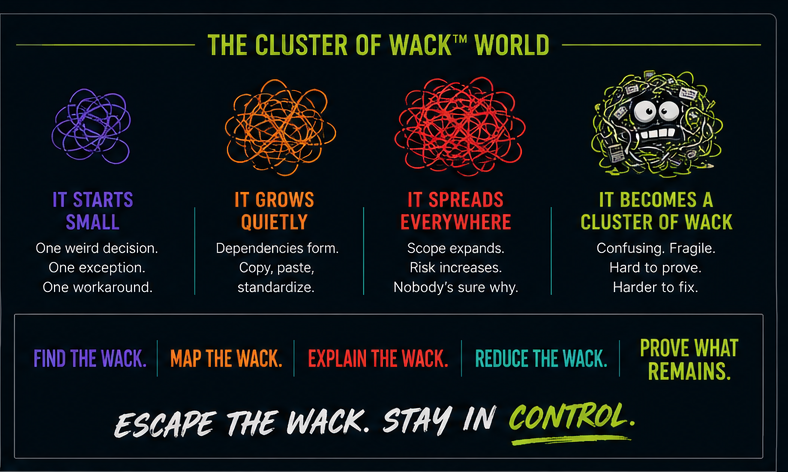
Surface the assumptions, exceptions, and mysterious “historical” decisions.
Diagram what touches what, where data flows, and how far the Wack travels.
Assign ownership and connect each dependency to the PCI DSS story.
Remove unnecessary complexity instead of documenting it forever.
Produce traceable evidence for what remains—and only what remains.
03 / Community session
A complete 45-minute practitioner session about the moment architecture, ownership, scope, and evidence stop telling the same story—with 30- and 60-minute variants ready for the room.
WACK-TALK-0001 / Speaker-ready draft
Why PCI DSS gets hard one reasonable decision at a time
Find the Wack. Map the Wack. Explain the Wack. Reduce the Wack. Prove what remains.
Independent practitioner education. Not PCI SSC terminology, not an assessment conclusion, and not affiliated with or endorsed by PCI SSC.
04 / Interactive diagnostic
This is a conversation starter, not an assessment conclusion. Select the signals that are true today and see where the architecture deserves attention first.
Signal checklist
05 / Composite stories
Six fictional composites. No client stories, no assessment theater—just the moment a reasonable explanation collides with the architecture around it.
A scope label held for eleven months. Then one maintenance window exposed the administrative path everybody had stopped seeing.
Open the case file
Every tile passed. The only thing missing was a shared understanding of what had actually been tested.
Open the case file
The document was current, authentic, and relevant to the provider. It still could not explain the customer’s half of the service.
Open the case file
The exception had an expiration date. The dependencies it attracted did not.
Open the case file
The architecture changed every month. The picture stayed beautiful for three years.
Open the case file
The evidence was copied so efficiently that nobody remembered what the original result had been created to prove.
Open the case file06 / Practitioner positions
Six substantial essays from the point where PCI DSS requirements meet architecture, operations, evidence, and accountable professional judgment.

Scott Norton / PCI DSS QSA | Johanson Group, LLP
A practitioner position is a reasoned professional analysis or recommendation—not PCI SSC language, not an organizational position unless identified as one, and not an assessment conclusion about a specific environment.
Be precise about where authority ends and practitioner judgment begins.
If a control only becomes legible during assessment week, the assessment may be operating the control instead of validating it.
“Show me what this looks like on Tuesday.”Read the position
A requirement becomes understandable when you can name what it protects, where it operates, and which relationships make it relevant.
“The requirement does not exist in isolation.”Read the position
Provider assurance matters. The customer still needs to understand the service, the allocation of responsibility, and the handoffs where assumptions accumulate.
“The vendor handles that is the beginning of a question, not the end of one.”Read the position
Compliance labels are conclusions. The useful work is tracing each conclusion to the population, source, method, decision, and operating record beneath it.
“Show me the source of truth.”Read the position
A scope story that cannot absorb changes in assets, identities, providers, connections, software, and business processes is already becoming historical fiction.
“Scope is an architecture problem before it is an assessment problem.”Read the position
Automation should give practitioners better context, cleaner populations, and earlier signals—not disguise an unsupported conclusion as machine certainty.
“The tool should make the assessor better informed, not less responsible.”Read the position
07 / After-hours provocations
The uncomfortable things your control environment whispers after the meeting—tasteful double meanings, serious operating questions, and one useful move before breakfast.
Turn down the dashboard glow.
“Let’s talk about the relationship between what the policy says and what Tuesday knows.”Practitioner-created editorial shorthand / not PCI SSC terminology
“The policy is polished. I want the story people tell when the document is closed.”
A control can be beautifully documented and operationally fictional.
Continue the conversation“If the control has a soulmate, the program has a succession problem.”
Heroic operators are wonderful people and dangerous control architectures.
Continue the conversation“A dashboard can only be reassuring about the population it knows exists.”
The quietest asset may be absent, not healthy.
Continue the conversation“A screenshot has a timestamp. A conclusion needs a timeline.”
Current state is not the same thing as sustained operation.
Continue the conversation“The exception was free. Keeping it has become a subscription.”
Temporary decisions send recurring invoices in meetings, testing, and uncertainty.
Continue the conversation“Fear of removal is evidence of a dependency nobody has mapped.”
Nothing says ‘critical architecture’ quite like ‘we don’t know what will break.’
Continue the conversation“Last year’s screenshot remembers a control that may no longer exist.”
Familiar evidence is comforting precisely because nobody has to learn what changed.
Continue the conversation“A beautiful sample can be the best-looking part of the wrong population.”
Selection becomes persuasive only after variation becomes visible.
Continue the conversation“A room full of stakeholders is not the same thing as one decision owner.”
Consensus is lovely until the architecture needs an uncomfortable answer.
Continue the conversation“Closure is an event. Confidence is a relationship with time.”
A ticket can close while the condition quietly learns how to return.
Continue the conversation“Shared responsibility becomes suspicious when every consequence belongs to somebody else.”
The handoff is where accountability goes to disappear politely.
Continue the conversation“If compliance needs assessment season to wake it, it is not business as usual. It is an annual relationship.”
A sustainable program notices its own changes, failures, and unfinished business.
Continue the conversation08 / Fresh practitioner arguments
Six substantial positions about living readiness, first assessments, token-wise AI, pickleball, instrumented infrastructure, and trust marketing.
Fresh from the part of compliance that refuses to sit still.
“Make the operating truth easier to see, harder to lose, and safer to say out loud.”Practitioner position + practitioner method / named review pending
Readiness should be a living property of the operating model, not a temporary condition produced for an assessor.
“The assessment should arrive to find the story already awake.”Read the argument
A first-time assessed entity does not need condescension. It needs a truthful map, a shared vocabulary, and permission to discover what the questionnaire never taught it to ask.
“Everything is new except the deadline.”Read the argument
Use AI where structured context can reduce reconstruction and expose change—without asking a model to impersonate accountable professional judgment.
“Spend tokens where readiness gains memory, not where conclusions gain confidence theater.”Read the argument
Pickleball rewards the same habits sustainable compliance programs need: know the boundaries, control the pace, communicate early, and stop trying to smash every ball.
“Not every ball is yours, not every shot should be hard, and the kitchen is still a boundary even when nobody drew it on your spreadsheet.”Read the argument
The strongest evidence is often a designed byproduct of operating the environment—not an artifact reconstructed when the assessment asks whether the control happened.
“What if the infrastructure could explain what changed, who changed it, which population was affected, and whether the control noticed?”Read the argument
Trust marketing becomes durable when the public assurance claim, the scoped service, the operating control, and the supporting evidence tell the same story.
“Do not let the landing page make a compliance promise the evidence room cannot recognize.”Read the argument
09 / Source intelligence
Keep ROC and SAQ decisions connected to the current Standard, reporting instructions, FAQs, supplements, program guidance, and the entity that must accept the result.
The acceptance boundary
Four Council FAQs expose one durable operating boundary across validation method, requirement applicability, partial assessments, and reporting.
10 / From the field
124 practical playbooks for moving from a memorable diagnosis to a shared map, a defensible decision, and traceable evidence.
Accumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookA system considered both in and out of scope depending on which evidence request is being answered.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookA configuration nobody currently owns and everyone is afraid to change.
Open the playbookThe growing distance between the environment that exists and the diagrams used to explain it.
Open the playbookThe quiet expansion of an exception beyond its original time, systems, owners, or approved conditions.
Open the playbookA convincing sample drawn from a population whose completeness and variants were never established.
Open the playbookAttempting to transform an unresolved applicability question into an exclusion by changing its spreadsheet status to N/A.
Open the playbookThe same underlying artifact repeated across control claims until repetition is mistaken for corroboration.
Open the playbookThe growing distance between the environment that exists and the diagrams used to explain it.
Open the playbookA system considered both in and out of scope depending on which evidence request is being answered.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookHow far one questionable component or dependency expands PCI DSS scope.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookA configuration nobody currently owns and everyone is afraid to change.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookThe growing distance between the environment that exists and the diagrams used to explain it.
Open the playbookThe extra operational and assessment effort created by unnecessary complexity.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookTwo control activities treated as interchangeable because their labels look alike while their coverage does not.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookThe quiet expansion of an exception beyond its original time, systems, owners, or approved conditions.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookTreating a scope label in a worksheet as the reasoning that makes the label true.
Open the playbookA convincing sample drawn from a population whose completeness and variants were never established.
Open the playbookA convincing sample drawn from a population whose completeness and variants were never established.
Open the playbookThe quiet expansion of an exception beyond its original time, systems, owners, or approved conditions.
Open the playbookThe growing distance between the environment that exists and the diagrams used to explain it.
Open the playbookA convincing sample drawn from a population whose completeness and variants were never established.
Open the playbookA system considered both in and out of scope depending on which evidence request is being answered.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookThe belief that a green tool result is equivalent to understanding what was tested and why it matters.
Open the playbookTwo control activities treated as interchangeable because their labels look alike while their coverage does not.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookThe growing distance between the environment that exists and the diagrams used to explain it.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookPresenting adjacent safeguards as a compensating control without demonstrating the required constraint, rigor, and equivalence.
Open the playbookTreating a scope label in a worksheet as the reasoning that makes the label true.
Open the playbookTreating a scope label in a worksheet as the reasoning that makes the label true.
Open the playbookThe same underlying artifact repeated across control claims until repetition is mistaken for corroboration.
Open the playbookTreating a scope label in a worksheet as the reasoning that makes the label true.
Open the playbookTreating a scope label in a worksheet as the reasoning that makes the label true.
Open the playbookTreating a scope label in a worksheet as the reasoning that makes the label true.
Open the playbookTreating a scope label in a worksheet as the reasoning that makes the label true.
Open the playbookThe same underlying artifact repeated across control claims until repetition is mistaken for corroboration.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookThe growing distance between the environment that exists and the diagrams used to explain it.
Open the playbookHow far one questionable component or dependency expands PCI DSS scope.
Open the playbookThe same underlying artifact repeated across control claims until repetition is mistaken for corroboration.
Open the playbookA system considered both in and out of scope depending on which evidence request is being answered.
Open the playbookA configuration nobody currently owns and everyone is afraid to change.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookHow far one questionable component or dependency expands PCI DSS scope.
Open the playbookHow far one questionable component or dependency expands PCI DSS scope.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookA convincing sample drawn from a population whose completeness and variants were never established.
Open the playbookA configuration nobody currently owns and everyone is afraid to change.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookA configuration nobody currently owns and everyone is afraid to change.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookWhen “the vendor handles it” substitutes for a mapped PCI DSS responsibility model.
Open the playbookReconstructing control operation from scattered remnants because no evidence chain was designed into the work.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookA convincing sample drawn from a population whose completeness and variants were never established.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookPresenting adjacent safeguards as a compensating control without demonstrating the required constraint, rigor, and equivalence.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookA convincing sample drawn from a population whose completeness and variants were never established.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookA responsibility model with many participants but no person accountable for the current decision or result.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookAccumulated complexity that makes an environment difficult to understand, secure, assess, or prove.
Open the playbookField series / W/ Operations Desk
Five linked briefs for the PCI clock, the operating index, card acceptance, year-end readiness, and the claims ledger—with practical downloads built for the work.
A green task completed on the wrong day is still a missed obligation. PCI time is not a collection of annual reminders; it is a set of evidence-bearing intervals that keep moving whether the assessment workspace is open or not.
Open the brief
Your inventory, diagrams, scans, penetration tests, critical tools, control records, and assessment evidence are not separate deliverables. They are different views of the same environment, and every material component must be traceable across them.
Open the brief
The first card payment is not merely a feature launch. It begins an operating commitment to understand the payment journey, protect account data, govern providers, maintain controls, preserve evidence, and answer to the organization that accepts your compliance validation.
Open the brief
The calendar does not become a control because everybody is out of office. Evidence windows keep moving, remediation still needs decisions, providers still have lead times, and assessors take time off too.
Open the brief
A claims ledger is the connective tissue between what the assessed entity says, what the assessor tests, what the evidence actually covers, and what the report is allowed to conclude.
Open the brief
A function can finish before the evidence request is written. A container can disappear before the assessor sees it. The assessment obligation does not disappear with the runtime.
Open the briefThe CDE may occupy one corner of the environment. Entra ID can still hold the keys to the doors, the badge printer, the emergency entrance, and several robots nobody invited to the access review.
Open the brief
The application uses the special call that withholds track data. The reader can still answer the ordinary call that returns it. Which interface did the control actually remove?
Open the brief
No breach. No outage. No fraud anyone noticed. So why are you asking me to prove the control worked? Because a quiet year is an outcome, not a test of how the year was operated.
Open the brief
You proved it last year. The assessor saw it. The ticket closed. Then the environment, population, period, owner, provider, or testing question changed. Which part of last year's conclusion do you believe survived unchanged?
Open the brief
If your evidence package contains only clean scans, completed reviews, resolved tickets, and perfect samples, I do not see a mature control environment. I see a story with the operating friction edited out.
Open the brief
If your platform's PCI implementation is a requirement library, a crosswalk, due dates, evidence uploads, and a green dashboard, the product ended where the assessment begins.
Open the brief
You cannot scan last quarter today. You can recover the facts, perform the control correctly now, repair the operating process, and present an honest assessment record. That is not the same as making the missed occurrence disappear.
Open the brief
An asset list can tell you what exists. A scope graph can tell you why it matters, what it can affect, which claim depends on it, and what must reopen when it changes.
Open the briefA penetration-test report proves that somebody tested something. Your methodology must explain why those targets, positions, layers, techniques, exclusions, dates, and retests were capable of testing the PCI claim you made.
Open the briefIf the final report is where the entity first learns what its penetration-testing methodology was, the methodology did not govern the test. The report merely narrated the work after the choices were already made.
Open the briefA PCI policy is not the Standard rewritten in your letterhead, a template with the company name replaced, or a promise that controls exist somewhere else. It is management's operating instruction for how this entity will satisfy, govern, and prove its obligations.
Open the briefA data-flow diagram gives account data a route. A data-flow narrative gives every route a transaction, condition, data state, owner, and consequence. If the arrow cannot be spoken as a complete testable sentence, it may be decoration.
Open the briefDevelopment can prove that a control can work there. It cannot automatically prove that the production control did work here, against the required population, during the required period.
Open the brief
A compliance integration can be unable to change one setting and still hold a privileged map of the identities, controls, vulnerabilities, and management plane surrounding the CDE. Read-only describes an operation. It does not finish the scope analysis.
Open the brief
An AI agent does not become PCI compliant because it speaks politely, invokes a payment tool, or never prints a full account number in the transcript. The assessable object is the exact service architecture that captures, routes, influences, logs, and returns the payment result.
Open the brief
Your ISV can build an elegant payment integration and still hand you a sentence that is impossible to assess: We are PCI certified. Certified as what, for which product or service, under which standard, covering which version and responsibilities?
Open the brief
Windows servicing now asks an organization to move quickly against known vulnerabilities while cumulative releases, out-of-band corrections, eligibility rules, restarts, application dependencies, and known issues can turn the security update into a production change with its own blast radius. That is a reason to engineer the control—not a reason to surrender it.
Open the brief
PCI DSS does not become business as usual because a policy says it is continuous. It becomes business as usual when scope, ownership, execution, evidence, testing, exceptions, change, and claims keep turning the same operating system.
Open the brief
A requirement number is an address in the Standard. It is not a complete model of the environment, the data, the control, the people, the evidence, the test, or the reason the work exists.
Open the brief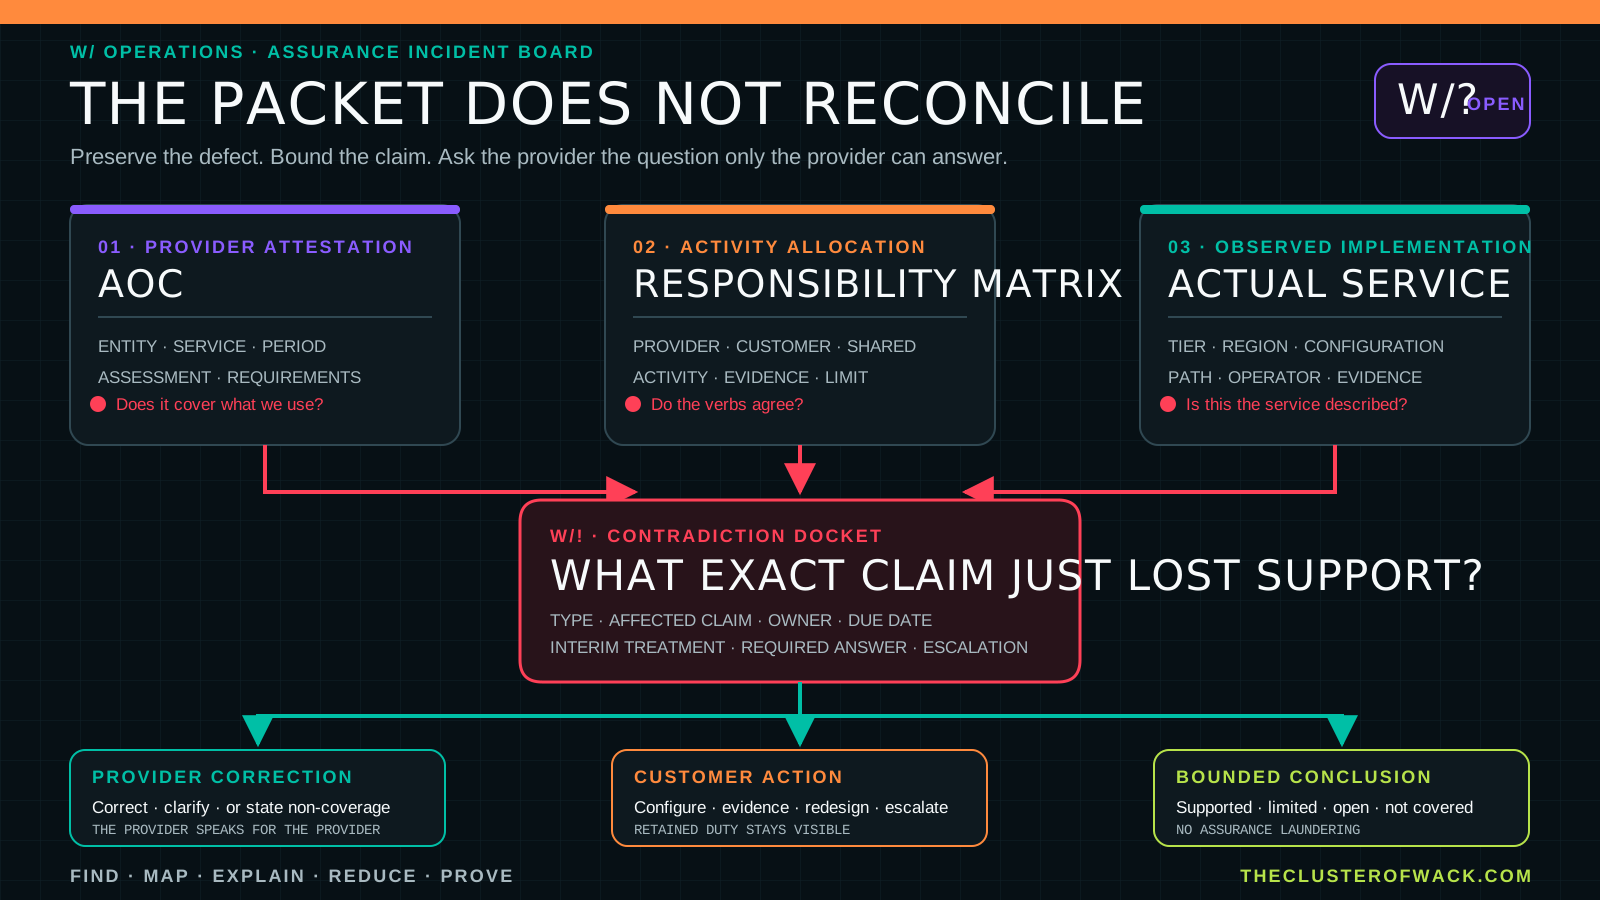
A current AOC and a polished responsibility matrix can still be unusable for your exact claim. The dangerous move is not noticing the flaw. The dangerous move is noticing it—and continuing as if the packet said what everyone needed it to say.
Open the brief
Five columns. One control. If they are all green, there is a fair chance somebody collapsed five different questions into one status.
Open the briefThe new mapping says one PCI DSS requirement relates to one NIST CSF outcome. Your dashboard says inherited. Your assessor still needs to know what you implemented, where it operated, what was tested, and what the evidence supports.
Open the briefA beautifully named screenshot can still be anonymous, untimed, unbounded, transformed, and impossible to defend.
Open the briefYour homepage is not your public attack surface. It is merely the public endpoint everyone remembered to name.
Open the briefYou deferred card capture to Twilio, then forgot the application Twilio calls next.
Open the briefConfidence is not a control. Tenure is not a constraint. A persuasive meeting is not a Compensating Controls Worksheet.
Open the briefTCP 443 is a service fact. TLS enabled is a configuration claim. Cryptographic viability is a maintained decision. Stop letting one impersonate the others.
Open the briefYou may keep the product quiet. You still need an internally complete account of the payment architecture, security influence, ownership, evidence, and change.
Open the briefPCI DSS transparency does not require a company to turn its ROC Executive Summary or AOC into a product architecture document, a competitive intelligence brief, or an attacker handbook.
Open the briefNot launched is a product-status sentence. It does not tell an assessor what exists, what is reachable, what can be activated, what already influences payment security, or what changes when the switch is thrown.
Open the briefZero revenue is a business fact. It is not an architecture description, a PCI DSS scope conclusion, a validation instruction, or permission to discover the payment boundary after the first transaction.
Open the briefThe cheapest PCI scope reduction happens while the payment architecture is still erasable. After launch, every shortcut acquires customers, evidence obligations, rollback anxiety, and somebody prepared to call it indispensable.
Open the briefA row in a validation instrument tells you what must be answered. It does not, by itself, prove that the requirement's predicate is true in this environment—or that an unsupported N/A is acceptable.
Open the briefA promise can govern tomorrow's work. It cannot become evidence that today's control is implemented, operating, and ready for the result being reported.
Open the briefGap discovery is part of assessment. Fault-pointing theater is not. The difference is whether the assessor leaves behind a bounded, supportable, actionable assessment record—or merely a bruise.
Open the briefA screenshot can faithfully show what was visible and still leave the reviewer unable to identify the subject, population, source, method, time, or claim.
Open the briefW/ FIELD TRAINING / NEW
W/ A Mole is a twelve-burrow reasoning exercise. Each signal is familiar. Your job is to choose the first move that turns confidence into a testable PCI story.
Start the Dependency Hunt
What's new / 2026-10-09
An interactive fictional case lets readers inspect five mismatches across engagement direction, payment flow, population, ownership, and operating history—without pretending to produce a readiness score or compliance conclusion.
See every new tool and releaseComplexity is not evidence. A checkbox is not architecture.